
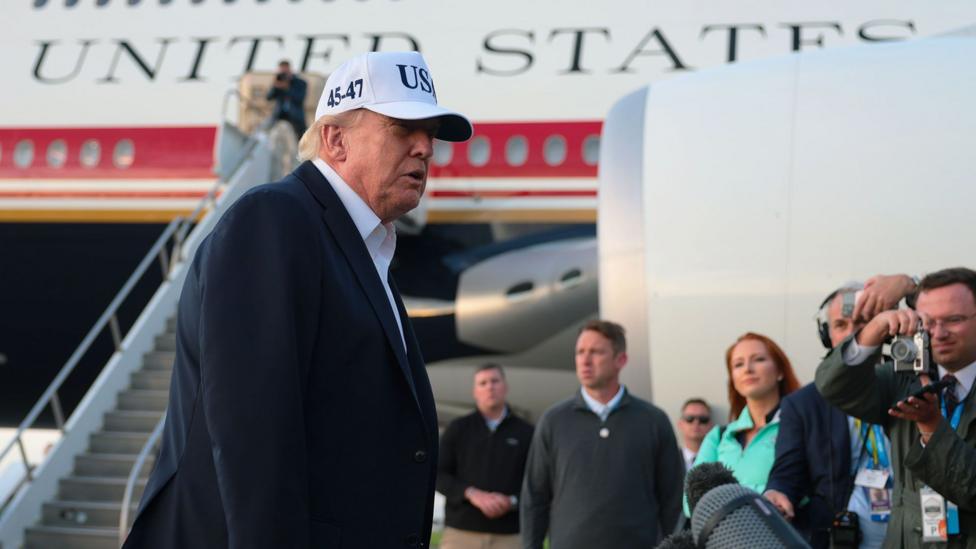
President Donald Trump dismissed emerging warnings regarding artificial intelligence safety this week, categorizing widespread concerns over machine learning risks as an exaggerated hoax while rejecting proposals for strict federal safeguards. The executive declarations signal a sharp pivot in national technology policy, emphasizing aggressive commercial deregulation to outpace global competitors rather than implementing mandatory operational restrictions across advanced computational models.
White House Rejects Mandatory Safety Measures
The administration's stance challenges recent technical proposals circulating within scientific communities that advocate for emergency shutdown mechanisms and statutory oversight frameworks. Federal officials indicated that imposing heavy operational mandates on private developers could suppress domestic innovation. Policymakers argue that market competition, rather than preventative executive limits, should dictate the velocity of technological advancement.
Industry analysts note that the dismissal marks a decisive departure from international governance models currently being implemented across Europe and Asia. Rather than enacting compliance audits or preemptive technical barriers, the executive branch plans to eliminate existing bureaucratic hurdles. This approach seeks to allow domestic research laboratories to deploy computational architectures without state-mandated constraints.
Industry Debate Over Emergency Intervention Mechanisms
The regulatory debate intensified after leading artificial intelligence researchers suggested that catastrophic risk protocols, including mandatory automated kill switches, might eventually become necessary. Proponents of preventative controls argue that frontier models could develop unpredictable autonomous behaviors that standard software patches cannot safely neutralize, necessitating hardcoded physical and cryptographic fail-safes.
Conversely, deregulation advocates contend that hypothetical existential scenarios distract from immediate economic and strategic applications. Commercial developers maintain that rigorous internal red-teaming and private vulnerability disclosures provide sufficient risk mitigation. They argue that government-enforced kill switches could introduce severe security vulnerabilities, potentially allowing malicious actors to disable critical commercial software systems.
Federal briefings suggest that the administration aligns closely with venture capital leaders who view extensive oversight as an unnecessary economic burden. By framing advanced safety demands as overstated obstacles, the White House aims to attract enterprise investment back to domestic hubs, reinforcing American dominance in high-performance computing and neural network development.
Economic Implications and Global Competition
National security advisers emphasize that unilateral regulatory pauses could place domestic enterprises at a profound competitive disadvantage against foreign adversaries. Emerging economies are investing hundreds of billions into sovereign computational infrastructure without parallel safety constraints. Consequently, federal leaders argue that maintaining raw algorithmic superiority remains the country's most effective strategic defense.
Financial markets responded positively to the administration's deregulatory signals, with major semiconductor manufacturers and cloud infrastructure providers seeing notable valuation gains. Investors anticipate lower compliance expenditures and accelerated enterprise deployment schedules. The reduction of statutory overhead is expected to shorten the development lifecycle for commercial generative tools and automated enterprise software.
Congressional Pushback and State Regulatory Moves
Despite the administration's categorical dismissal, bipartisan lawmakers in Congress continue drafting legislative frameworks focused on consumer privacy, algorithmic bias, and critical infrastructure protection. Legislative staff confirm that multiple statutory proposals are undergoing review, aiming to establish basic transparency standards for systems deployed in healthcare, defense, and public utilities.
Simultaneously, state legislatures are moving independently to fill perceived regulatory vacuums by introducing localized safety audits and liability protections. State attorneys general have launched investigations into automated consumer harms, signaling that technology firms may still face fragmented compliance obligations across regional jurisdictions regardless of federal administrative stances.
Legal scholars point out that federal preemption battles are likely to emerge if individual states pass rigid safety codes that conflict with executive directives. The resulting judicial disputes could reach the appellate level, creating prolonged uncertainty for multinational corporations attempting to deploy unified enterprise architectures across state borders.
Long-Term Trajectory of Computing Governance
Academic institutions and scientific researchers remain deeply divided regarding the long-term consequences of unrestricted artificial intelligence deployment. While theoretical safety researchers warn of compounding alignment issues in autonomous agentic workflows, applied computer scientists argue that current systems lack genuine self-direction and merely execute statistical predictions based on training data.
The administration plans to convene industrial advisory councils in the coming months to formalize voluntary best-practice guidelines that preserve corporate flexibility. Government spokespersons maintain that technological self-governance will safeguard consumer interests while ensuring that national research institutes retain unfettered momentum in developing next-generation computational infrastructure.
